Several reports have indicated data leakage from ChatGPT ever since its release by the Microsoft-backed OpenAI in November 2022. Additionally, threat actors have been abusing the platform to gain unauthorized access or leak sensitive and confidential data. However, ChatGPT has released a new ChatGPT enterprise version, which is claimed to be SOC 2 compliant with […]
The post OpenAI Released ChatGPT Enterprise With SOC 2 Compliant & Data Encryption appeared first on Cyber Security News.
https://cybersecuritynews.com/chatgpt-enterprise-data-encryption/?utm_source=dlvr.it&utm_medium=blogger
Thursday, August 31, 2023
Wednesday, August 30, 2023
Citrix NetScaler Alert: Ransomware Hackers Exploiting Critical Vulnerability
Unpatched Citrix NetScaler systems exposed to the internet are being targeted by unknown threat actors in what's suspected to be a ransomware attack.
Cybersecurity company Sophos is tracking the activity cluster under the moniker STAC4663.
Attack chains involve the exploitation of CVE-2023-3519, a critical code injection vulnerability impacting NetScaler ADC and Gateway servers that could
https://thehackernews.com/2023/08/citrix-netscaler-alert-ransomware.html?utm_source=dlvr.it&utm_medium=blogger
Tuesday, August 29, 2023
Kroll Suffers Data Breach as Employee Falls Victim to SIM Swap Hack
A high-profile cyber attack targeted a prominent company, Kroll. This attack utilized a sophisticated technique known as “SIM swapping,” which allowed the threat actor to gain unauthorized access to sensitive personal information. On Saturday, August 19, 2023, Kroll was informed about the SIM swapping attack that targeted a T-Mobile US., Inc. account belonging to a Kroll […]
The post Kroll Suffers Data Breach as Employee Falls Victim to SIM Swap Hack appeared first on Cyber Security News.
https://cybersecuritynews.com/kroll-data-breach-sim-swap-attack/?utm_source=dlvr.it&utm_medium=blogger
Monday, August 28, 2023
What true diversity in the cybersecurity industry looks like
In this Help Net Security video, Larry Whiteside, Jr., CISO at RegScale and President of Cyversity, discusses how, now more than ever, the cybersecurity industry needs the diversity of thought to address the increasingly complex and technology-driven challenges organizations face.…
Read more →
The post What true diversity in the cybersecurity industry looks like first appeared on IT Security News.
https://www.itsecuritynews.info/what-true-diversity-in-the-cybersecurity-industry-looks-like/?utm_source=dlvr.it&utm_medium=blogger
Sunday, August 27, 2023
Threat and Vulnerability Roundup for the week of August 20th to 26th
Welcome to the Threat and Vulnerability Roundup, a weekly publication from Cyber Writes that provides the most recent news on cybersecurity. Use our wide coverage to stay up to date. Critical flaws, exploits, and recent techniques for attacking have all been highlighted. We also offer the most latest software upgrades to keep your devices safe. […]
The post Threat and Vulnerability Roundup for the week of August 20th to 26th appeared first on Cyber Security News.
https://cybersecuritynews.com/weekly-roundup-august-20th/?utm_source=dlvr.it&utm_medium=blogger
Saturday, August 26, 2023
Urgent FBI Warning: Barracuda Email Gateways Vulnerable Despite Recent Patches
The U.S. Federal Bureau of Investigation (FBI) is warning that Barracuda Networks Email Security Gateway (ESG) appliances patched against a recently disclosed critical flaw continue to be at risk of potential compromise from suspected Chinese hacking groups.
It also deemed the fixes as "ineffective" and that it "continues to observe active intrusions and considers all affected Barracuda ESG
https://thehackernews.com/2023/08/urgent-fbi-warning-barracuda-email.html?utm_source=dlvr.it&utm_medium=blogger
Friday, August 25, 2023
Kali Linux 2023.3 Released – What’s New!
Kali Linux is a free and open-source Linux-based operating system that is mainly dedicated to fulfilling two prime criteria:- In short, this OS, Kali Linux, is one of the most advanced Debian-derived Linux distributions that was originally developed and maintained by Offensive Security. Offensive Security recently launched Kali Linux 2023.3 with several new mods, changes, […]
The post Kali Linux 2023.3 Released – What’s New! appeared first on Cyber Security News.
https://cybersecuritynews.com/kali-linux-2023-3/?utm_source=dlvr.it&utm_medium=blogger
Thursday, August 24, 2023
Over a Dozen Malicious npm Packages Target Roblox Game Developers
More than a dozen malicious packages have been discovered on the npm package repository since the start of August 2023 with capabilities to deploy an open-source information stealer called Luna Token Grabber on systems belonging to Roblox developers.
The ongoing campaign, first detected on August 1 by ReversingLabs, employs modules that masquerade as the legitimate package noblox.js, an API
https://thehackernews.com/2023/08/over-dozen-malicious-npm-packages.html?utm_source=dlvr.it&utm_medium=blogger
Wednesday, August 23, 2023
Carderbee Attacks: Hong Kong Organizations Targeted via Malicious Software Updates
A previously undocumented threat cluster has been linked to a software supply chain attack targeting organizations primarily located in Hong Kong and other regions in Asia.
The Symantec Threat Hunter Team, part of Broadcom, is tracking the activity under its insect-themed moniker Carderbee.
The attacks, per the cybersecurity firm, leverage a trojanized version of a legitimate software called
https://thehackernews.com/2023/08/carderbee-attacks-hong-kong.html?utm_source=dlvr.it&utm_medium=blogger
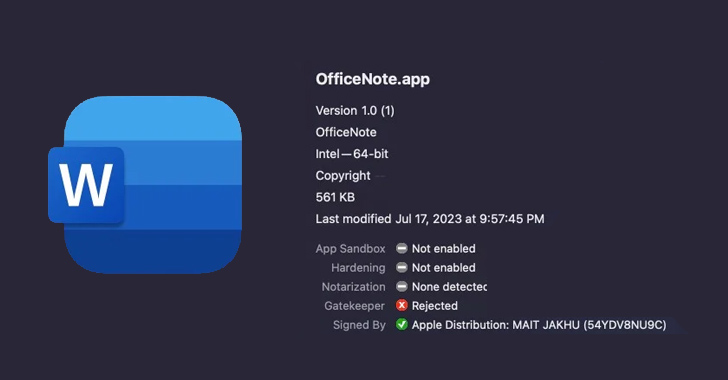
New Variant of XLoader macOS Malware Disguised as 'OfficeNote' Productivity App
A new variant of an Apple macOS malware called XLoader has surfaced in the wild, masquerading its malicious features under the guise of an office productivity app called "OfficeNote."
"The new version of XLoader is bundled inside a standard Apple disk image with the name OfficeNote.dmg," SentinelOne security researchers Dinesh Devadoss and Phil Stokes said in a Monday analysis. "The application
https://thehackernews.com/2023/08/new-variant-of-xloader-macos-malware.html?utm_source=dlvr.it&utm_medium=blogger
Subscribe to:
Posts (Atom)