Wednesday, May 31, 2023

Over 421,000,000 Times Installed Android Apps from Google Play Contain Malware

A spyware-enabled Android app module that can gather details about files kept on devices and send them to attackers. Additionally, clipboard contents can be replaced and uploaded to a remote server. “This malicious SDK collects information on files stored on Android devices and can transfer them to attackers; it can also substitute and upload clipboard […] The post Over 421,000,000 Times Installed Android Apps from Google Play Contain Malware appeared first on Cyber Security News.
https://cybersecuritynews.com/spyware-enabled-android-app/?utm_source=dlvr.it&utm_medium=blogger

Tuesday, May 30, 2023

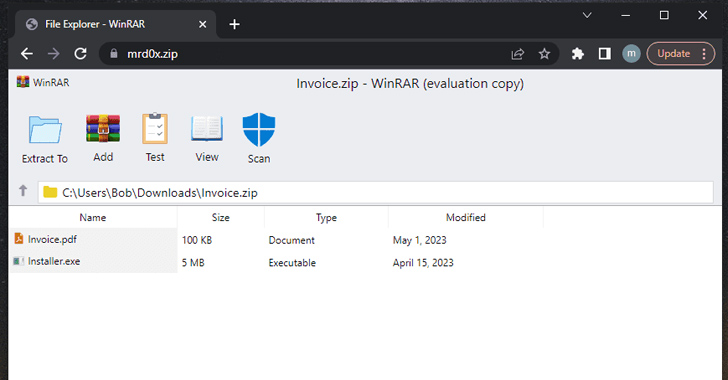
Don't Click That ZIP File! Phishers Weaponizing .ZIP Domains to Trick Victims

A new phishing technique called "file archiver in the browser" can be leveraged to "emulate" a file archiver software in a web browser when a victim visits a .ZIP domain. "With this phishing attack, you simulate a file archiver software (e.g., WinRAR) in the browser and use a .zip domain to make it appear more legitimate," security researcher mr.d0x disclosed last week. Threat actors, in a
https://thehackernews.com/2023/05/dont-click-that-zip-file-phishers.html?utm_source=dlvr.it&utm_medium=blogger

Monday, May 29, 2023

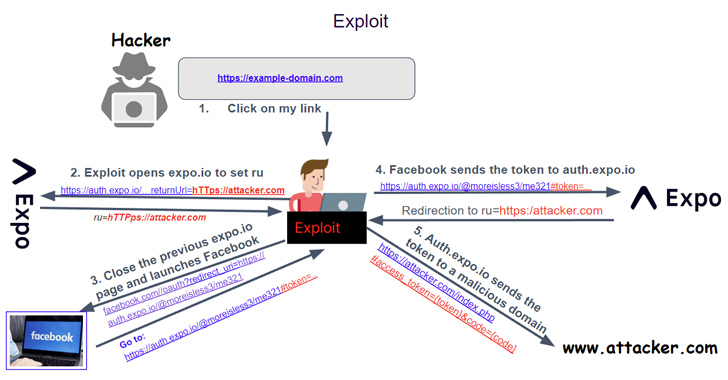
Critical OAuth Framework Flaw Let Attackers Hijack Accounts & Steal Sensitive Data

OAuth Flaw in Expo Platform affects hundreds of Third-Party sites, apps. An attacker can exploit this vulnerability in the expo framework by sending a malicious link to a victim. The post Critical OAuth Framework Flaw Let Attackers Hijack Accounts & Steal Sensitive Data appeared first on Cyber Security News.
https://cybersecuritynews.com/oauth-framework-flaw/?utm_source=dlvr.it&utm_medium=blogger
Sunday, May 28, 2023

Critical OAuth Vulnerability in Expo Framework Allows Account Hijacking

A critical security vulnerability has been disclosed in the Open Authorization (OAuth) implementation of the application development framework Expo.io. The shortcoming, assigned the CVE identifier CVE-2023-28131, has a severity rating of 9.6 on the CVSS scoring system. API security firm Salt Labs said the issue rendered services using the framework susceptible to credential leakage, which could
https://thehackernews.com/2023/05/critical-oauth-vulnerability-in-expo.html?utm_source=dlvr.it&utm_medium=blogger
Saturday, May 27, 2023

New COSMICENERGY Malware Exploits ICS Protocol to Sabotage Power Grids

A new strain of malicious software that's engineered to penetrate and disrupt critical systems in industrial environments has been unearthed. Google-owned threat intelligence firm Mandiant dubbed the malware COSMICENERGY, adding it was uploaded to the VirusTotal public malware scanning utility in December 2021 by a submitter in Russia. There is no evidence that it has been put to use in the wild
https://thehackernews.com/2023/05/new-cosmicenergy-malware-exploits-ics.html?utm_source=dlvr.it&utm_medium=blogger
Friday, May 26, 2023

China's Stealthy Hackers Infiltrate U.S. and Guam Critical Infrastructure Undetected

A stealthy China-based group managed to establish a persistent foothold into critical infrastructure organizations in the U.S. and Guam without being detected, Microsoft and the "Five Eyes" nations said on Wednesday. The tech giant's threat intelligence team is tracking the activity, which includes post-compromise credential access and network system discovery, under the name Volt Typhoon. The
https://thehackernews.com/2023/05/chinas-stealthy-hackers-infiltrate-us.html?utm_source=dlvr.it&utm_medium=blogger
Thursday, May 25, 2023

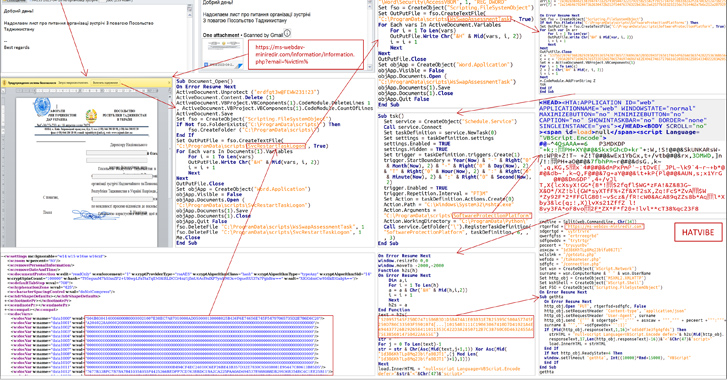
Cyber Attacks Strike Ukraine's State Bodies in Espionage Operation

The Computer Emergency Response Team of Ukraine (CERT-UA) has warned of cyber attacks targeting state bodies in the country as part of an espionage campaign. The intrusion set, attributed to a threat actor tracked by the authority as UAC-0063 since 2021, leverages phishing lures to deploy a variety of malicious tools on infected systems. The origins of the hacking crew are presently unknown. In
https://thehackernews.com/2023/05/cyber-attacks-strike-ukraines-state.html?utm_source=dlvr.it&utm_medium=blogger
Wednesday, May 24, 2023

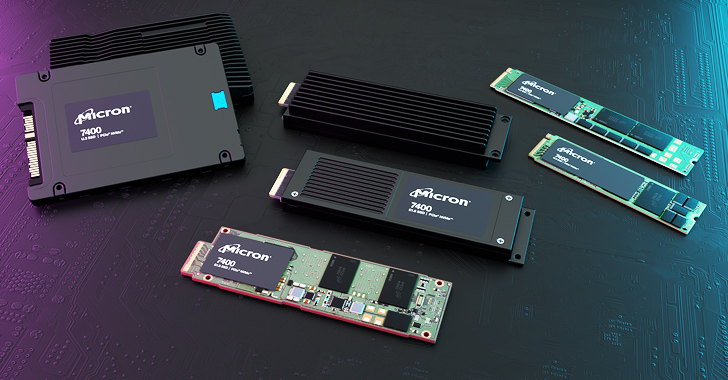
China Bans U.S. Chip Giant Micron, Citing "Serious Cybersecurity Problems"

China has banned U.S. chip maker Micron from selling its products to Chinese companies working on key infrastructure projects, citing national security risks. The development comes nearly two months after the country's cybersecurity authority initiated a probe in late March 2023 to assess potential network security risks. "The purpose of this network security review of Micron's products is to
https://thehackernews.com/2023/05/china-bans-us-chip-giant-micron-citing.html?utm_source=dlvr.it&utm_medium=blogger
Tuesday, May 23, 2023

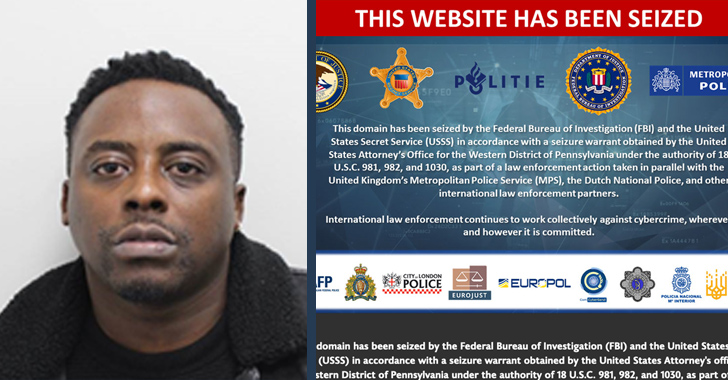
U.K. Fraudster Behind iSpoof Scam Receives 13-Year Jail Term for Cyber Crimes

A U.K. national responsible for his role as the administrator of the now-defunct iSpoof online phone number spoofing service has been sentenced to 13 years and 4 months in prison. Tejay Fletcher, 35, of Western Gateway, London, was awarded the sentence on May 18, 2023. He pleaded guilty last month to a number of cyber offenses, including facilitating fraud and possessing and transferring
https://thehackernews.com/2023/05/uk-fraudster-behind-ispoof-scam.html?utm_source=dlvr.it&utm_medium=blogger
Monday, May 22, 2023

PyPI Repository Under Attack: User Sign-Ups and Package Uploads Temporarily Halted

The maintainers of Python Package Index (PyPI), the official third-party software repository for the Python programming language, have temporarily disabled the ability for users to sign up and upload new packages until further notice. "The volume of malicious users and malicious projects being created on the index in the past week has outpaced our ability to respond to it in a timely fashion,
https://thehackernews.com/2023/05/pypi-repository-under-attack-user-sign.html?utm_source=dlvr.it&utm_medium=blogger