Wednesday, July 5, 2023

Neo_Net Hackers Group Targeting Users of Prominent Banks Globally

A Spanish-based threat actor Neo_Net has conducted campaigns against financial institutions and banks and achieved the highest success rate in spite of its unsophisticated tools. The campaign has compromised a significant amount of Personally Identifiable Information (PII), including telephone numbers, national identity numbers, and names of thousands of victims. Neo_Net has established and rented out […] The post Neo_Net Hackers Group Targeting Users of Prominent Banks Globally appeared first on Cyber Security News.
https://cybersecuritynews.com/neo_net-targeting-bank-users/?utm_source=dlvr.it&utm_medium=blogger
Tuesday, July 4, 2023

Evasive Meduza Stealer Targets 19 Password Managers and 76 Crypto Wallets

In yet another sign of a lucrative crimeware-as-a-service (CaaS) ecosystem, cybersecurity researchers have discovered a new Windows-based information stealer called Meduza Stealer that's actively being developed by its author to evade detection by software solutions. "The Meduza Stealer has a singular objective: comprehensive data theft," Uptycs said in a new report. "It pilfers users' browsing
https://thehackernews.com/2023/07/evasive-meduza-stealer-targets-19.html?utm_source=dlvr.it&utm_medium=blogger
Monday, July 3, 2023

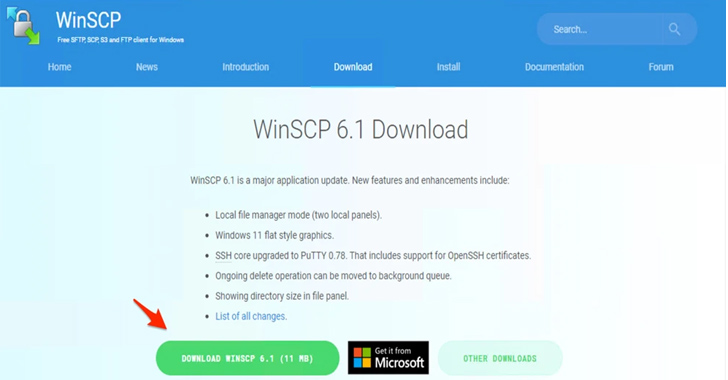
BlackCat Operators Distributing Ransomware Disguised as WinSCP via Malvertising

Threat actors associated with the BlackCat ransomware have been observed employing malvertising tricks to distribute rogue installers of the WinSCP file transfer application. "Malicious actors used malvertising to distribute a piece of malware via cloned webpages of legitimate organizations," Trend Micro researchers said in an analysis published last week. "In this case, the distribution
https://thehackernews.com/2023/07/blackcat-operators-distributing.html?utm_source=dlvr.it&utm_medium=blogger

Sunday, July 2, 2023

The High School Changed Every Student’s Password to ‘Ch@ngeme!’

In an attempt to reset the student’s passwords after a mistake in a cybersecurity audit, the Oak Park and River Forest (OPRF) High School reset all the students’ passwords to ‘Ch@ngeme!’ During a cybersecurity audit on the school’s systems, an unexpected vendor error resettled all the students’ passwords that prevented all the 3000+ students from […] The post The High School Changed Every Student’s Password to ‘Ch@ngeme!’ appeared first on Cyber Security News.
https://cybersecuritynews.com/school-changed-students-password/?utm_source=dlvr.it&utm_medium=blogger

Saturday, July 1, 2023

Top 10 Best AWS Security Tools – 2023

To store the data with high standard security, there several AWS security tools are available to manage, scan, and audit the data that’s been stored. AWS is nothing but Amazon Web Services, which is undoubtedly revolutionary and implemented by millions of businesses around the world to store and manage data. It has the ability to […] The post Top 10 Best AWS Security Tools – 2023 appeared first on Cyber Security News.
https://cybersecuritynews.com/aws-security-tools/?utm_source=dlvr.it&utm_medium=blogger

University of Manchester Hack – Over One Million NHS patient data Exposed

It has come to light that the University of Manchester fell victim to a Ransomware Hack, which resulted in the breach of 1.1 million NHS patients’ information from 200 hospitals. This event has caused great concern and raised important questions about data security. Ransomware is malicious software (malware) designed to lock devices and prevent users […] The post University of Manchester Hack – Over One Million NHS patient data Exposed appeared first on Cyber Security News.
https://cybersecuritynews.com/nhs-patient-data-exposed/?utm_source=dlvr.it&utm_medium=blogger
Friday, June 30, 2023

Critical Security Flaw in Social Login Plugin for WordPress Exposes Users' Accounts

A critical security flaw has been disclosed in miniOrange's Social Login and Register plugin for WordPress that could enable a malicious actor to log in as any user-provided information about email address is already known. Tracked as CVE-2023-2982 (CVSS score: 9.8), the authentication bypass flaw impacts all versions of the plugin, including and prior to 7.6.4. It was addressed on June 14, 2023
https://thehackernews.com/2023/06/critical-security-flaw-in-social-login.html?utm_source=dlvr.it&utm_medium=blogger
Thursday, June 29, 2023

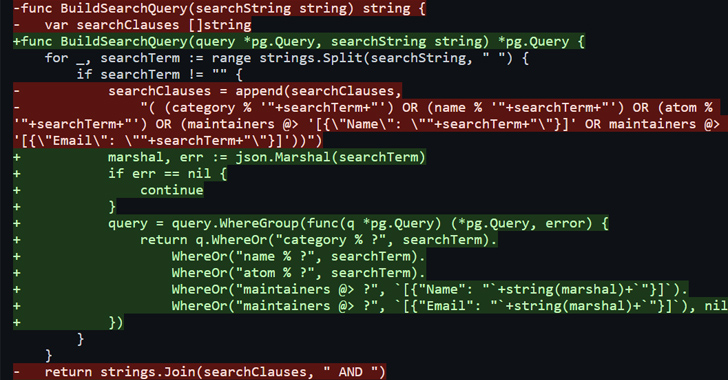
Critical SQL Injection Flaws Expose Gentoo Soko to Remote Code Execution

Multiple SQL injection vulnerabilities have been disclosed in Gentoo Soko that could lead to remote code execution (RCE) on vulnerable systems. "These SQL injections happened despite the use of an Object-Relational Mapping (ORM) library and prepared statements," SonarSource researcher Thomas Chauchefoin said, adding they could result in RCE on Soko because of a "misconfiguration of the database.
https://thehackernews.com/2023/06/critical-sql-injection-flaws-expose.html?utm_source=dlvr.it&utm_medium=blogger
Wednesday, June 28, 2023

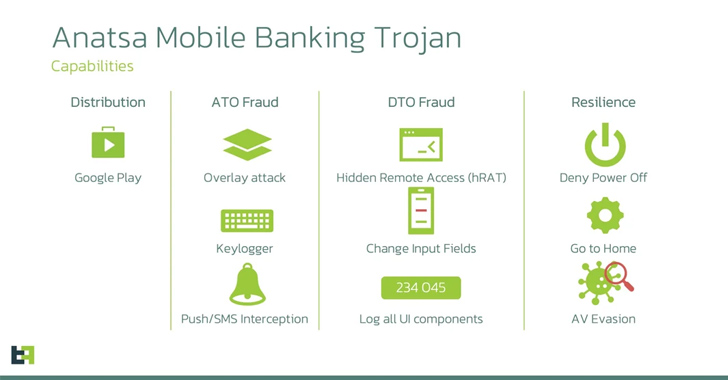
Anatsa Banking Trojan Targeting Users in US, UK, Germany, Austria, and Switzerland

A new Android malware campaign has been observed pushing the Anatsa banking trojan to target banking customers in the U.S., U.K., Germany, Austria, and Switzerland since the start of March 2023. "The actors behind Anatsa aim to steal credentials used to authorize customers in mobile banking applications and perform Device-Takeover Fraud (DTO) to initiate fraudulent transactions," ThreatFabric 
https://thehackernews.com/2023/06/anatsa-banking-trojan-targeting-users.html?utm_source=dlvr.it&utm_medium=blogger
Tuesday, June 27, 2023

Microsoft Warns of Widescale Credential Stealing Attacks by Russian Hackers

Microsoft has disclosed that it's detected a spike in credential-stealing attacks conducted by the Russian state-affiliated hacker group known as Midnight Blizzard. The intrusions, which made use of residential proxy services to obfuscate the source IP address of the attacks, target governments, IT service providers, NGOs, defense, and critical manufacturing sectors, the tech giant's threat
https://thehackernews.com/2023/06/microsoft-warns-of-widescale-credential.html?utm_source=dlvr.it&utm_medium=blogger