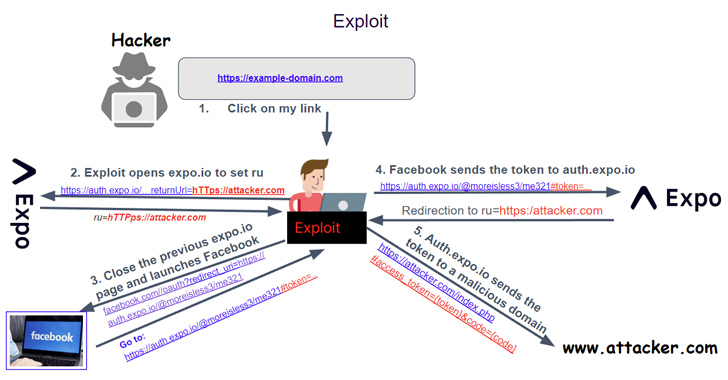
A critical security vulnerability has been disclosed in the Open Authorization (OAuth) implementation of the application development framework Expo.io.
The shortcoming, assigned the CVE identifier CVE-2023-28131, has a severity rating of 9.6 on the CVSS scoring system. API security firm Salt Labs said the issue rendered services using the framework susceptible to credential leakage, which could
https://thehackernews.com/2023/05/critical-oauth-vulnerability-in-expo.html?utm_source=dlvr.it&utm_medium=blogger
Sunday, May 28, 2023
Saturday, May 27, 2023
New COSMICENERGY Malware Exploits ICS Protocol to Sabotage Power Grids
A new strain of malicious software that's engineered to penetrate and disrupt critical systems in industrial environments has been unearthed.
Google-owned threat intelligence firm Mandiant dubbed the malware COSMICENERGY, adding it was uploaded to the VirusTotal public malware scanning utility in December 2021 by a submitter in Russia. There is no evidence that it has been put to use in the wild
https://thehackernews.com/2023/05/new-cosmicenergy-malware-exploits-ics.html?utm_source=dlvr.it&utm_medium=blogger
Friday, May 26, 2023
China's Stealthy Hackers Infiltrate U.S. and Guam Critical Infrastructure Undetected
A stealthy China-based group managed to establish a persistent foothold into critical infrastructure organizations in the U.S. and Guam without being detected, Microsoft and the "Five Eyes" nations said on Wednesday.
The tech giant's threat intelligence team is tracking the activity, which includes post-compromise credential access and network system discovery, under the name Volt Typhoon.
The
https://thehackernews.com/2023/05/chinas-stealthy-hackers-infiltrate-us.html?utm_source=dlvr.it&utm_medium=blogger
Thursday, May 25, 2023
Cyber Attacks Strike Ukraine's State Bodies in Espionage Operation
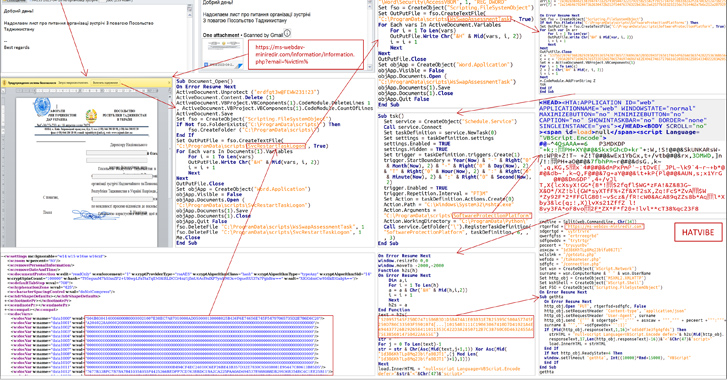
The Computer Emergency Response Team of Ukraine (CERT-UA) has warned of cyber attacks targeting state bodies in the country as part of an espionage campaign.
The intrusion set, attributed to a threat actor tracked by the authority as UAC-0063 since 2021, leverages phishing lures to deploy a variety of malicious tools on infected systems. The origins of the hacking crew are presently unknown.
In
https://thehackernews.com/2023/05/cyber-attacks-strike-ukraines-state.html?utm_source=dlvr.it&utm_medium=blogger
Wednesday, May 24, 2023
China Bans U.S. Chip Giant Micron, Citing "Serious Cybersecurity Problems"
China has banned U.S. chip maker Micron from selling its products to Chinese companies working on key infrastructure projects, citing national security risks.
The development comes nearly two months after the country's cybersecurity authority initiated a probe in late March 2023 to assess potential network security risks.
"The purpose of this network security review of Micron's products is to
https://thehackernews.com/2023/05/china-bans-us-chip-giant-micron-citing.html?utm_source=dlvr.it&utm_medium=blogger
Tuesday, May 23, 2023
U.K. Fraudster Behind iSpoof Scam Receives 13-Year Jail Term for Cyber Crimes
A U.K. national responsible for his role as the administrator of the now-defunct iSpoof online phone number spoofing service has been sentenced to 13 years and 4 months in prison.
Tejay Fletcher, 35, of Western Gateway, London, was awarded the sentence on May 18, 2023. He pleaded guilty last month to a number of cyber offenses, including facilitating fraud and possessing and transferring
https://thehackernews.com/2023/05/uk-fraudster-behind-ispoof-scam.html?utm_source=dlvr.it&utm_medium=blogger
Monday, May 22, 2023
PyPI Repository Under Attack: User Sign-Ups and Package Uploads Temporarily Halted
The maintainers of Python Package Index (PyPI), the official third-party software repository for the Python programming language, have temporarily disabled the ability for users to sign up and upload new packages until further notice.
"The volume of malicious users and malicious projects being created on the index in the past week has outpaced our ability to respond to it in a timely fashion,
https://thehackernews.com/2023/05/pypi-repository-under-attack-user-sign.html?utm_source=dlvr.it&utm_medium=blogger
Sunday, May 21, 2023
Notorious Cyber Gang FIN7 Returns With Cl0p Ransomware in New Wave of Attacks
The notorious cybercrime group known as FIN7 has been observed deploying Cl0p (aka Clop) ransomware, marking the threat actor's first ransomware campaign since late 2021.
Microsoft, which detected the activity in April 2023, is tracking the financially motivated actor under its new taxonomy Sangria Tempest.
"In these recent attacks, Sangria Tempest uses the PowerShell script POWERTRASH to load
https://thehackernews.com/2023/05/notorious-cyber-gang-fin7-returns-cl0p.html?utm_source=dlvr.it&utm_medium=blogger
Saturday, May 20, 2023
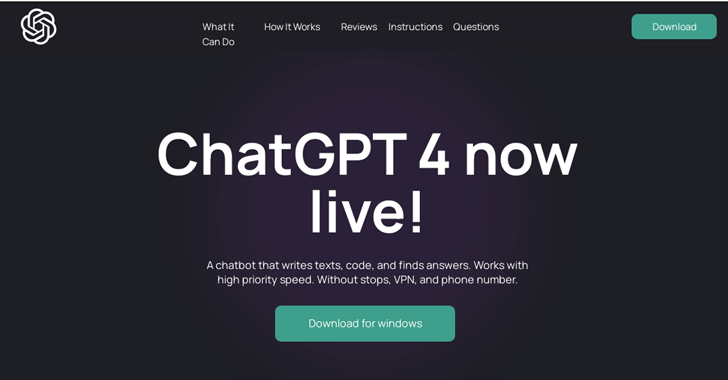
Searching for AI Tools? Watch Out for Rogue Sites Distributing RedLine Malware
Malicious Google Search ads for generative AI services like OpenAI ChatGPT and Midjourney are being used to direct users to sketchy websites as part of a BATLOADER campaign designed to deliver RedLine Stealer malware.
"Both AI services are extremely popular but lack first-party standalone apps (i.e., users interface with ChatGPT via their web interface while Midjourney uses Discord)," eSentire
https://thehackernews.com/2023/05/searching-for-ai-tools-watch-out-for.html?utm_source=dlvr.it&utm_medium=blogger
Friday, May 19, 2023
8220 Gang Exploiting Oracle WebLogic Flaw to Hijack Servers and Mine Cryptocurrency
The notorious cryptojacking group tracked as 8220 Gang has been spotted weaponizing a six-year-old security flaw in Oracle WebLogic servers to ensnare vulnerable instances into a botnet and distribute cryptocurrency mining malware.
The flaw in question is CVE-2017-3506 (CVSS score: 7.4), which, when successfully exploited, could allow an unauthenticated attacker to execute arbitrary commands
https://thehackernews.com/2023/05/8220-gang-exploiting-oracle-weblogic.html?utm_source=dlvr.it&utm_medium=blogger
Subscribe to:
Posts (Atom)


