Top-Level Domains (TLDs) have been extremely popular ever since the emergence of the internet. ICANN is the organization that is responsible for these TLD registrations. Domains ending with any characters like .xyz, .top, etc., are being registered by this ICANN. In addition to TLDs, there is a “gTLD” program in which companies can register their […]
The post Hackers are Actively Using the new.zip Domain for Malicious Attacks appeared first on Cyber Security News.
https://cybersecuritynews.com/zip-domain-for-malicious-attacks/?utm_source=dlvr.it&utm_medium=blogger
Thursday, May 18, 2023
Wednesday, May 17, 2023
Hackers Using Golang Variant of Cobalt Strike to Target Apple macOS Systems
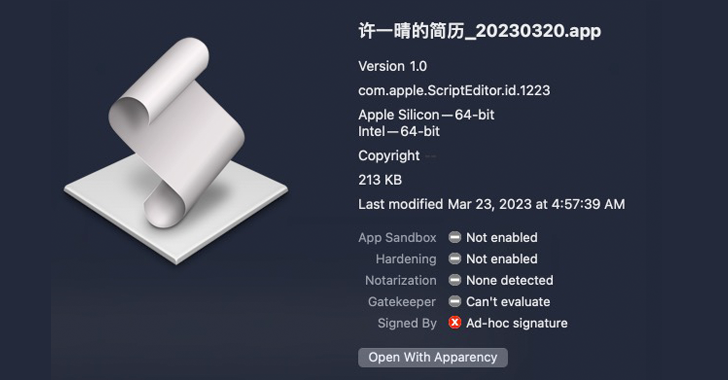
A Golang implementation of Cobalt Strike called Geacon is likely to garner the attention of threat actors looking to target Apple macOS systems.
That's according to findings from SentinelOne, which observed an increase in the number of Geacon payloads appearing on VirusTotal in recent months.
"While some of these are likely red-team operations, others bear the characteristics of genuine
https://thehackernews.com/2023/05/hackers-using-golang-variant-of-cobalt.html?utm_source=dlvr.it&utm_medium=blogger
Tuesday, May 16, 2023
BlackSuit Ransomware Attacks Windows and Linux Users
CRIL discovered a recently identified ransomware group called BlackSuit, which poses a threat to users of both widely used operating systems:- The Linux version of BlackSuit ransomware resembles the Royal ransomware while maintaining its distinct communication method through an onion site and refraining from disclosing any information about the victims. Technical Analysis BlackSuit ransomware, written […]
The post BlackSuit Ransomware Attacks Windows and Linux Users appeared first on Cyber Security News.
https://cybersecuritynews.com/blacksuit-ransomware/?utm_source=dlvr.it&utm_medium=blogger
Monday, May 15, 2023
How is information stored in cloud secure from hacks
The rise of cloud computing has provided individuals and businesses with a convenient way to store and access their data. However, with this convenience comes a concern about data security. Cloud storage services have become a target for hackers, and…
Read more →
The post How is information stored in cloud secure from hacks first appeared on IT Security News.
https://www.itsecuritynews.info/how-is-information-stored-in-cloud-secure-from-hacks/?utm_source=dlvr.it&utm_medium=blogger
Sunday, May 14, 2023
New Phishing-as-a-Service Platform Lets Cybercriminals Generate Convincing Phishing Pages
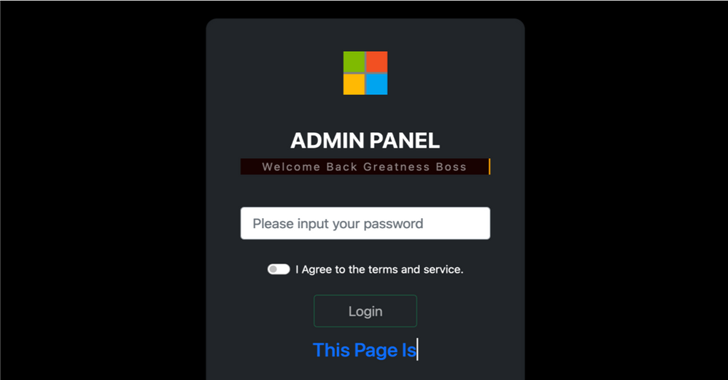
A new phishing-as-a-service (PhaaS or PaaS) platform named Greatness has been leveraged by cybercriminals to target business users of the Microsoft 365 cloud service since at least mid-2022, effectively lowering the bar to entry for phishing attacks.
"Greatness, for now, is only focused on Microsoft 365 phishing pages, providing its affiliates with an attachment and link builder that creates
https://thehackernews.com/2023/05/new-phishing-as-service-platform-lets.html?utm_source=dlvr.it&utm_medium=blogger
Saturday, May 13, 2023
Bl00dy Ransomware Gang Strikes Education Sector with Critical PaperCut Vulnerability
U.S. cybersecurity and intelligence agencies have warned of attacks carried out by a threat actor known as the Bl00dy Ransomware Gang that attempt to exploit vulnerable PaperCut servers against the education facilities sector in the country.
The attacks took place in early May 2023, the Federal Bureau of Investigation (FBI) and Cybersecurity and Infrastructure Security Agency (CISA) said in a
https://thehackernews.com/2023/05/bl00dy-ransomware-gang-strikes.html?utm_source=dlvr.it&utm_medium=blogger
Friday, May 12, 2023
Andoryu Botnet Exploits Critical Ruckus Wireless Flaw for Widespread Attack
A nascent botnet called Andoryu has been found to exploit a now-patched critical security flaw in the Ruckus Wireless Admin panel to break into vulnerable devices.
The flaw, tracked as CVE-2023-25717 (CVSS score: 9.8), stems from improper handling of HTTP requests, leading to unauthenticated remote code execution and a complete compromise of wireless Access Point (AP) equipment.
Andoryu was
https://thehackernews.com/2023/05/andoryu-botnet-exploits-critical-ruckus.html?utm_source=dlvr.it&utm_medium=blogger
Thursday, May 11, 2023
U.S. Government Neutralizes Russia's Most Sophisticated Snake Cyber Espionage Tool
The U.S. government on Tuesday announced the court-authorized disruption of a global network compromised by an advanced malware strain known as Snake wielded by Russia's Federal Security Service (FSB).
Snake, dubbed the "most sophisticated cyber espionage tool," is the handiwork of a Russian state-sponsored group called Turla (aka Iron Hunter, Secret Blizzard, SUMMIT, Uroburos, Venomous Bear,
https://thehackernews.com/2023/05/us-government-neutralizes-russias-most.html?utm_source=dlvr.it&utm_medium=blogger
Wednesday, May 10, 2023
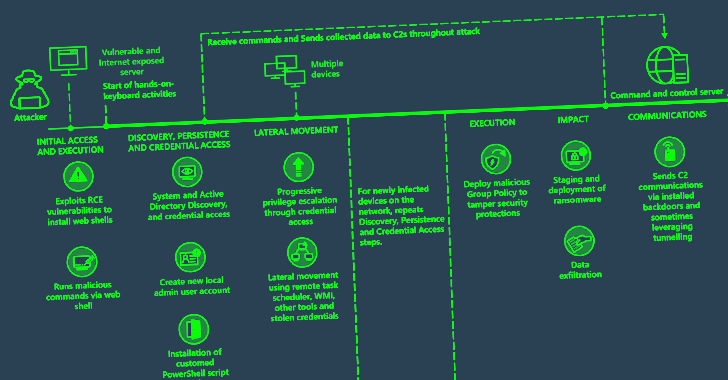
Microsoft Warns of State-Sponsored Attacks Exploiting Critical PaperCut Vulnerability
Iranian nation-state groups have now joined financially motivated actors in actively exploiting a critical flaw in PaperCut print management software, Microsoft disclosed over the weekend.
The tech giant's threat intelligence team said it observed both Mango Sandstorm (Mercury) and Mint Sandstorm (Phosphorus) weaponizing CVE-2023-27350 in their operations to achieve initial access.
"This
https://thehackernews.com/2023/05/microsoft-warns-of-state-sponsored.html?utm_source=dlvr.it&utm_medium=blogger
Tuesday, May 9, 2023
How to Set Up a Threat Hunting and Threat Intelligence Program
Threat hunting is an essential component of your cybersecurity strategy. Whether you're getting started or in an advanced state, this article will help you ramp up your threat intelligence program.
What is Threat Hunting?
The cybersecurity industry is shifting from a reactive to a proactive approach. Instead of waiting for cybersecurity alerts and then addressing them, security organizations are
https://thehackernews.com/2023/05/how-to-set-up-threat-hunting-and-threat.html?utm_source=dlvr.it&utm_medium=blogger
Subscribe to:
Posts (Atom)


