Monday, May 8, 2023

CERT-UA Warns of SmokeLoader and RoarBAT Malware Attacks Against Ukraine

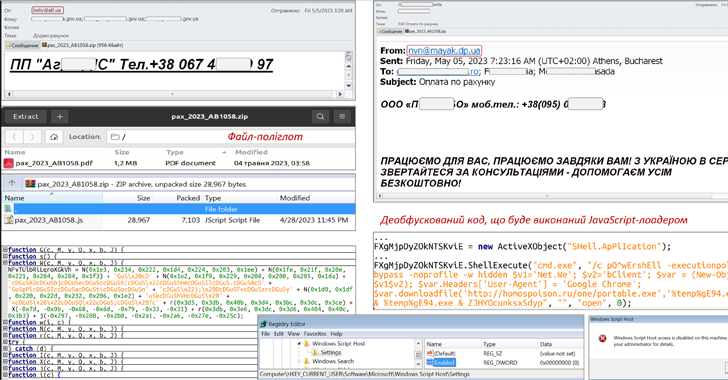
An ongoing phishing campaign with invoice-themed lures is being used to distribute the SmokeLoader malware in the form of a polyglot file, according to the Computer Emergency Response Team of Ukraine (CERT-UA). The emails, per the agency, are sent using compromised accounts and come with a ZIP archive that, in reality, is a polyglot file containing a decoy document and a JavaScript file. The
https://thehackernews.com/2023/05/cert-ua-warns-of-smokeloader-and.html?utm_source=dlvr.it&utm_medium=blogger

Sunday, May 7, 2023

Ex-Uber CSO Avoids Prison Time for Concealing Data Breach

On Wednesday, an ex-Uber CSO was found guilty of federal charges related to payments he secretly approved to hackers who broke into the ride-hailing company in 2016. For concealing the breach from the Federal Trade Commission, which was looking into Uber’s privacy measures at the time, Joe Sullivan was found guilty of obstructing justice and […] The post Ex-Uber CSO Avoids Prison Time for Concealing Data Breach appeared first on Cyber Security News.
https://cybersecuritynews.com/ex-uber-cso-avoids-prison-time/?utm_source=dlvr.it&utm_medium=blogger

Over 2 Million WordPress Websites Exposed to XSS Attacks

Patchstack security researchers recently warned that ‘Advanced Custom Fields’ and ‘Advanced Custom Fields Pro’ WordPress plugins are at risk of cross-site scripting attacks (XSS).  These WP plugins, installed on millions of websites, may be vulnerable to security breaches. The ‘Advanced Custom Fields’ and ‘Advanced Custom Fields Pro’ plugins are renowned custom field builders for WordPress […] The post Over 2 Million WordPress Websites Exposed to XSS Attacks appeared first on Cyber Security News.
https://cybersecuritynews.com/over-2-million-wordpress-websites-exposed-to-xss-attacks/?utm_source=dlvr.it&utm_medium=blogger

Dragon Breath APT Group Using Double-Clean-App Technique to Target Gambling Industry

An advanced persistent threat (APT) actor known as Dragon Breath has been observed adding new layers of complexity to its attacks by adopting a novel DLL side-loading mechanism. "The attack is based on a classic side-loading attack, consisting of a clean application, a malicious loader, and an encrypted payload, with various modifications made to these components over time," Sophos researcher
https://thehackernews.com/2023/05/dragon-breath-apt-group-using-double.html?utm_source=dlvr.it&utm_medium=blogger

Saturday, May 6, 2023

Fleckpe Android Malware Sneaks onto Google Play Store with Over 620,000 Downloads

A new Android subscription malware named Fleckpe has been unearthed on the Google Play Store, amassing more than 620,000 downloads in total since 2022. Kaspersky, which identified 11 apps on the official app storefront, said the malware masqueraded as legitimate photo editing apps, camera, and smartphone wallpaper packs. The apps have since been taken down. The operation primarily targets users
https://thehackernews.com/2023/05/fleckpe-android-malware-sneaks-onto.html?utm_source=dlvr.it&utm_medium=blogger

Friday, May 5, 2023

Meta Takes Down Malware Campaign That Used ChatGPT as a Lure to Steal Accounts

Meta said it took steps to take down more than 1,000 malicious URLs from being shared across its services that were found to leverage OpenAI's ChatGPT as a lure to propagate about 10 malware families since March 2023. The development comes against the backdrop of fake ChatGPT web browser extensions being increasingly used to steal users' Facebook account credentials with an aim to run
https://thehackernews.com/2023/05/meta-takes-down-malware-campaign-that.html?utm_source=dlvr.it&utm_medium=blogger

Thursday, May 4, 2023

Hackers Exploiting 5-year-old Unpatched Vulnerability in TBK DVR Devices

Threat actors are actively exploiting an unpatched five-year-old flaw impacting TBK digital video recording (DVR) devices, according to an advisory issued by Fortinet FortiGuard Labs. The vulnerability in question is CVE-2018-9995 (CVSS score: 9.8), a critical authentication bypass issue that could be exploited by remote actors to gain elevated permissions. "The 5-year-old vulnerability (
https://thehackernews.com/2023/05/hackers-exploiting-5-year-old-unpatched.html?utm_source=dlvr.it&utm_medium=blogger

Wednesday, May 3, 2023

North Korea's ScarCruft Deploys RokRAT Malware via LNK File Infection Chains

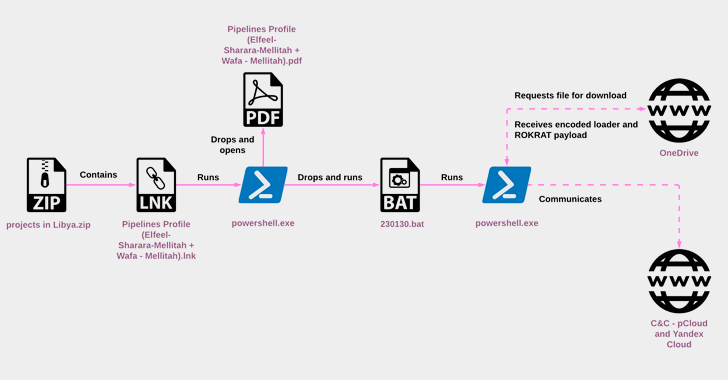
The North Korean threat actor known as ScarCruft started experimenting with oversized LNK files as a delivery route for RokRAT malware as early as July 2022, the same month Microsoft began blocking macros across Office documents by default. "RokRAT has not changed significantly over the years, but its deployment methods have evolved, now utilizing archives containing LNK files that initiate
https://thehackernews.com/2023/05/north-koreas-scarcruft-deploys-rokrat.html?utm_source=dlvr.it&utm_medium=blogger

Tuesday, May 2, 2023

SDP vs VPN: Which is the Best Security Solution for Enterprise Business in 2023

Introduction As organizations move towards digitization, security has become a significant part of their operations. Software-Defined Perimeter (SDP) and Virtual Private Networks (VPN) are two of the most extensively used security solutions on the market. Although both solutions provide substantial security advantages, their operation is distinct. SDP is a security system that restricts network access […] The post SDP vs VPN: Which is the Best Security Solution for Enterprise Business in 2023 appeared first on Cyber Security News.
https://cybersecuritynews.com/sdp-vs-vpn/?utm_source=dlvr.it&utm_medium=blogger
Monday, May 1, 2023

Google Blocks 1.43 Million Malicious Apps, Bans 73,000 Bad Accounts in 2022

Google disclosed that its improved security features and app review processes helped it block 1.43 million bad apps from being published to the Play Store in 2022. In addition, the company said it banned 173,000 bad accounts and fended off over $2 billion in fraudulent and abusive transactions through developer-facing features like Voided Purchases API, Obfuscated Account ID, and Play Integrity
https://thehackernews.com/2023/05/google-blocks-143-million-malicious.html?utm_source=dlvr.it&utm_medium=blogger